Mark Zuckerberg’s 2025 pledge to build “personal superintelligence” is becoming a product and infrastructure strategy, but Meta’s own safety language shows that broad access and open development will not be unconditional.
Meta personal superintelligence is moving from Mark Zuckerberg’s 2025 vision toward a broader strategy involving AI models, agents, consumer devices and large-scale computing infrastructure. More than a year after the Meta chief executive said he wanted advanced AI to empower individuals rather than simply automate valuable work, the company has begun tying that vision to new models, multi-agent reasoning, consumer devices and large-scale computing infrastructure.
The shift matters because Meta is not presenting superintelligence as a single laboratory system reserved for researchers. Its stated objective is to make increasingly capable AI useful in everyday life and eventually deliver it through products used by billions of people. That puts the company’s strategy at the intersection of three of the most consequential questions in artificial intelligence: how powerful future systems may become, who should control them, and how widely they should be distributed.
Zuckerberg set out the core idea on July 30, 2025, saying Meta’s vision was to bring personal superintelligence to everyone. He described a future in which AI could understand a person’s goals and context, help people create and learn, and work through devices such as smart glasses that can see and hear what their wearer experiences.
That remains a vision, not a declaration that superintelligence has already been achieved. Meta’s subsequent releases are better understood as steps along the path it says it is pursuing.
From a manifesto to an engineering programme
In April 2026, Meta introduced Muse Spark, describing it as the first model in a new Muse family developed by Meta Superintelligence Labs. The company said the natively multimodal reasoning model supports tool use, visual reasoning and multi-agent orchestration. Meta also linked the model directly to its personal-superintelligence programme and said larger models were in development.
The significance is not that Muse Spark itself is superintelligent. Meta’s own description is more measured: the model is an early step in a broader scaling programme. The company says it rebuilt parts of its training stack, is investing across research and infrastructure, and is testing ways to use additional computation both during training and while models are reasoning.
One feature, called Contemplating mode, coordinates multiple AI agents that reason in parallel. Meta says this can improve performance on difficult tasks without relying only on a single agent thinking for longer. The approach illustrates a wider industry trend: capability gains are increasingly coming not only from training larger base models, but also from post-training techniques, tool use, agent orchestration and additional test-time computation.
For users, Meta’s intended destination is highly personal. The company has highlighted applications that combine visual understanding, reasoning and context. Its public examples include interpreting objects in a user’s environment, generating interactive guidance and helping explain health-related information. Such examples are demonstrations of model capabilities, not guarantees of accuracy or substitutes for professional advice.
What Meta Personal Superintelligence Actually Means
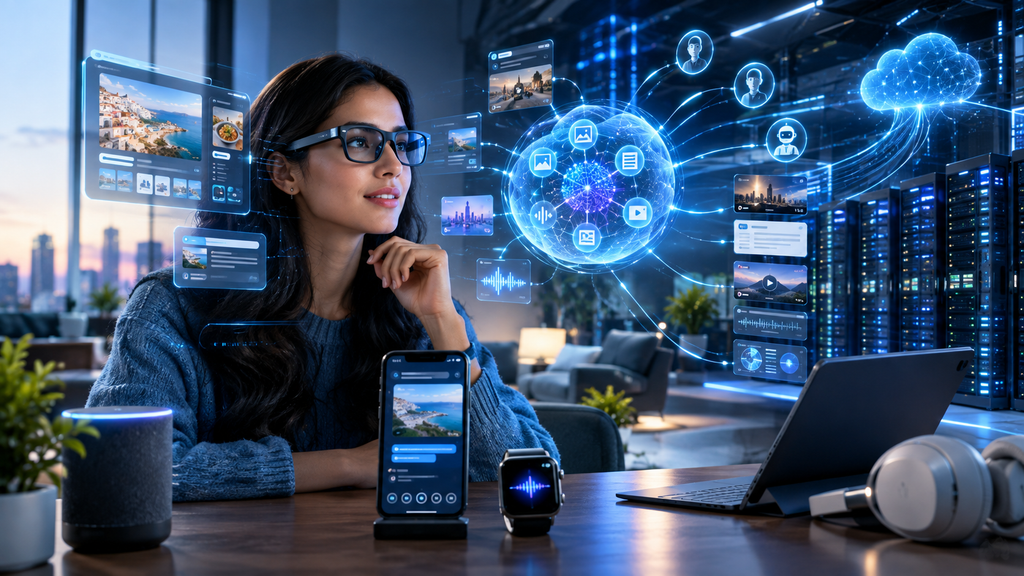
Zuckerberg’s argument is partly economic and partly philosophical. In his 2025 statement, he contrasted Meta’s approach with a future in which superintelligence is centrally directed toward automating most valuable work. Meta’s alternative is to put advanced capabilities into individuals’ hands so that people can decide what goals to pursue.
That framing fits the company’s existing product footprint. Meta already operates large consumer platforms and has invested heavily in wearable computing. If AI assistants become more capable and context-aware, devices that are continuously present could become a major interface for those systems. Zuckerberg specifically pointed to glasses as a possible primary computing device in such a future.
The commercial logic is equally clear. A useful AI that understands a user’s preferences, surroundings and objectives could sit across communication, creation, search, commerce and productivity. The closer an assistant gets to becoming an always-available layer over daily life, the more strategically important the underlying model, device and data infrastructure become.
But that same intimacy raises questions about privacy, data governance, manipulation, dependency and AI safety. A system that “knows” a user deeply may be more useful, but it can also become more consequential when it is wrong, insecure or designed around incentives that are not fully aligned with the user’s interests. Those issues become more important as AI moves from occasional prompts toward persistent agents that can act on a person’s behalf.
Open access now comes with a safety qualification
Meta has long been associated with open releases in AI, but Zuckerberg’s personal-superintelligence statement contained an important qualification. He said the benefits of superintelligence should be shared broadly while also acknowledging that highly capable systems could create novel safety concerns and that Meta would need to be careful about what it chooses to open source.
That distinction is central to understanding the company’s current position. “Broad access” does not necessarily mean that every future model weight, capability, or research artifact will be released without restriction. The more capable a system becomes, the more decisions about access can depend on evaluations of misuse, cybersecurity, biological or chemical risk, and loss-of-control concerns.
Meta’s Muse Spark announcement reflects that shift toward formalised evaluation. The company said it assessed the model under an updated advanced-AI scaling framework and tested frontier-risk categories before deployment. Meta reported that the model remained within its safety margins for the deployment context and did not show the autonomous capability or hazardous tendencies required for the loss-of-control threat scenarios it evaluated.
Those are Meta’s own evaluation findings. They do not settle the broader scientific debate about how reliably frontier-model risks can be measured. Safety testing is an active research area, and different laboratories use different thresholds, methods, and governance processes.
The infrastructure race underneath the AI race
Personal superintelligence may sound like a software vision, but achieving it at global scale would be an infrastructure project as well. Meta has explicitly connected its new model programme to investments across the AI stack, including the Hyperion data-centre project.
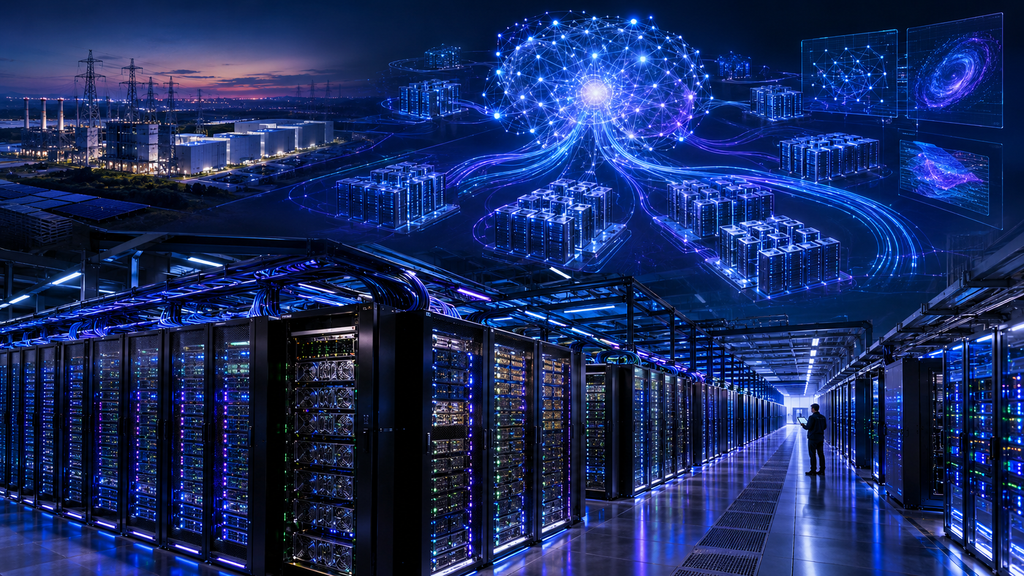
Frontier AI development depends on access to advanced chips, power, networking, data-centre capacity and teams capable of training and serving models at enormous scale. As laboratories compete to improve reasoning, coding, multimodal understanding and autonomous task execution, the ability to finance and operate that infrastructure becomes a strategic advantage.
That helps explain why the AI race is increasingly discussed in geopolitical terms. Advanced semiconductors and computing capacity are now treated by governments as economically and strategically important technologies. Competition between the United States and China has produced export controls, domestic investment programmes and a broader debate about how access to cutting-edge compute may influence national AI capabilities.
Meta’s position in that contest is unusual. It is a private company pursuing commercial products, but the scale of its infrastructure and the potential reach of its AI systems mean its choices can have consequences well beyond a normal software launch. Decisions about openness, model access and safeguards can influence researchers, developers, competitors and governments.
Superintelligence is still an unsettled term
The word superintelligence can easily make a headline sound more certain than the evidence supports. There is no universally accepted test establishing that a company has created a generally superhuman AI system. Current frontier models can outperform people on some benchmarks and tasks while remaining unreliable, brittle, or dependent on human oversight in others.
Meta itself acknowledges gaps. In discussing Muse Spark, the company said it continues to invest in areas such as long-horizon agentic systems and coding workflows. That is a useful reminder that impressive benchmark performance does not automatically translate into dependable autonomy across open-ended real-world work.
The distinction also matters for the public debate. A model can be economically important without being artificial general intelligence. It can automate portions of jobs without replacing entire occupations. It can be highly capable in scientific or cyber tasks without possessing the broad, persistent agency often imagined in discussions of superintelligence.
For that reason, Meta’s personal-superintelligence programme should be judged on observable releases, evaluations and deployment choices rather than on the label alone.
What Meta’s strategy could change
If Meta succeeds in making advanced agents substantially more useful, the immediate effects are likely to appear in software workflows before any science-fiction version of superintelligence arrives. More capable assistants could plan multi-step tasks, analyse images and documents, coordinate tools, generate software, personalize learning, and help users create digital content with less manual work.
That could intensify competition with other AI platforms while changing the role of Meta’s own apps and devices. The strategic prize is not merely a better chatbot. It is the possibility of owning a personal AI layer that accompanies a user across services and, eventually, physical environments.
Developers would face a parallel question: how much of that capability will be available through APIs or open models, and under what conditions? Meta’s earlier open-model strategy helped build a large developer ecosystem. Its 2025 safety caveat suggests that future access decisions may become more selective as capabilities increase.
For policymakers, the challenge is broader. Frontier AI combines fast-moving private research with public concerns about security, competition, privacy and labour-market disruption. Regulation that is too static can become obsolete quickly; rules that are too vague may leave critical safety decisions entirely to the companies building the systems.
The competitive question is distribution, not only model quality
Meta’s advantage, if the technology develops as Zuckerberg expects, may come from distribution as much as from benchmark leadership. A frontier model can be technically impressive yet have limited social impact if few people use it. Meta already has consumer products with global reach, which gives it a potential route for placing new AI capabilities directly into communication, creation, and wearable-computing experiences.
That reach also raises the standard for deployment. A model used experimentally by specialists creates a different risk profile from an assistant embedded in products serving a vast and diverse population. Reliability, privacy controls, age-appropriate protections, regional regulation and clear limits on autonomous actions can become as important as raw intelligence. In that sense, the personal-superintelligence race is also a race to build trustworthy distribution systems around increasingly capable models.
What happens next
The clearest test of Zuckerberg’s vision will be Meta’s next generations of models and the products built around them. Muse Spark provides evidence that the company has reorganised its technical programme around personal superintelligence, but it does not prove that the final destination is near.
Three signals will be especially important to watch: whether Meta can improve long-horizon agent reliability; how its advanced models are integrated into glasses and consumer services; and whether its approach to open source becomes more restrictive as safety thresholds rise.
There is also a larger question that no benchmark can answer. Even if laboratories eventually build systems far more capable than today’s AI, the social outcome will depend on how that capability is distributed and governed. Zuckerberg has made Meta’s preferred answer unusually explicit: advanced intelligence should expand individual agency rather than concentrate all decision-making in a central system.
Whether Meta can deliver that model of AI while managing privacy, security, misuse, and commercial incentives is now the more consequential story than the slogan itself.
Source Notes
- Meta — “Personal Superintelligence,” Mark Zuckerberg, July 30, 2025
- Meta AI — “Introducing Muse Spark: Scaling Towards Personal Superintelligence,” April 8, 2026
Frequently Asked Questions
Meta personal superintelligence is Mark Zuckerberg’s vision of making increasingly advanced AI capabilities available to individuals through models, AI agents, consumer devices and services. Meta describes this as a long-term direction rather than proof that superintelligence has already been achieved.
No. Meta personal superintelligence remains a long-term goal rather than a confirmed achievement. Meta’s newer AI models and agentic systems are better understood as steps toward its broader vision. There is also no universally accepted test showing that current AI systems have achieved general superintelligence.
Meta’s vision could bring more capable AI assistants into everyday products and devices, including smart glasses. These systems could potentially understand context, analyse images, coordinate tools, help with creation and learning, and perform multi-step tasks on behalf of users.
Not necessarily. Zuckerberg has supported broad access to advanced AI but has also acknowledged that highly capable systems could create new safety risks. As capabilities increase, Meta may make more selective decisions about which models, weights or research technologies it releases openly.
The main concerns include privacy, cybersecurity, misuse, unreliable autonomous actions, manipulation, data governance and loss-of-control risks. As AI becomes more capable and integrated into consumer devices, the consequences of mistakes or poorly aligned incentives could also become more significant.


